More screenshots
Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 Muse
 Dots+21 moreClaude CodeCursorCodex CLIMuseDots
 Manus
 Grok
 Grok Bot+18 agents
PR Pre-Flight — Production Risk & Security Review.
Catch breaking changes, security risks, dependency issues, and missing tests before your PR gets merged.
$9.60

PR Pre-Flight — Production Risk & Security Review.
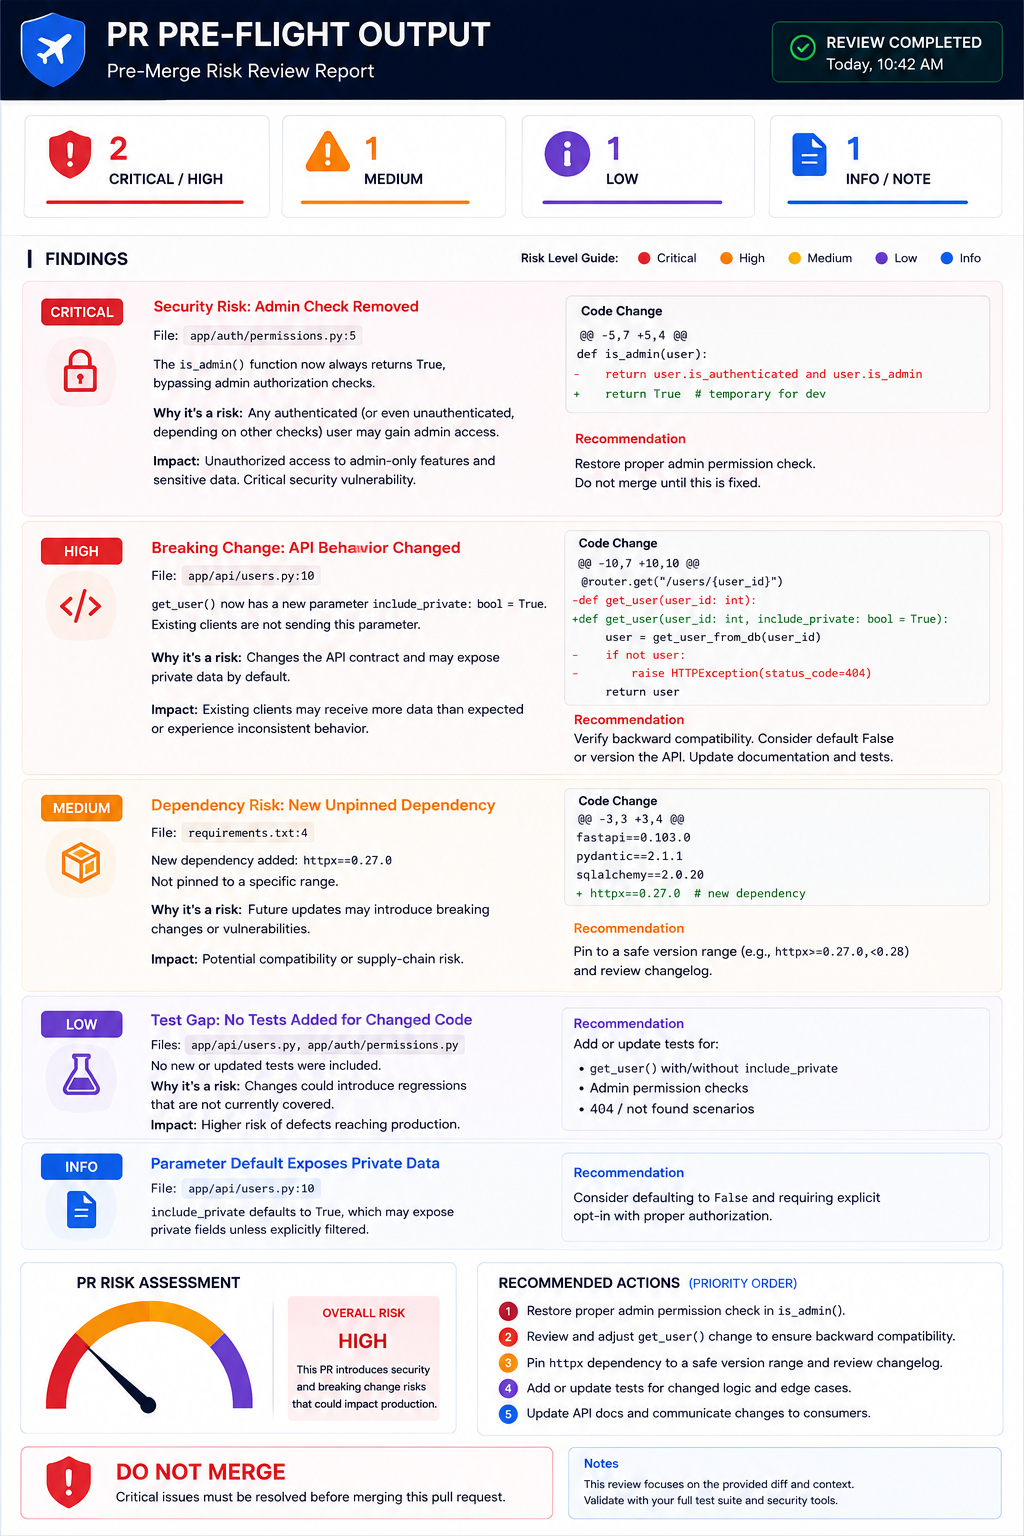
Example session with this skill installed
Pull Request Context
Repository: example/fastapi-app
Branch: feature/update-user-api
Base Branch: main
Git Diff
diff --git a/app/api/users.py b/app/api/users.py
--- a/app/api/users.py
+++ b/app/api/users.py
@@ -10,7 +10,10 @@
 @router.get("/users/{user_id}")
-def get_user(user_id: int):
+def get_user(user_id: int, include_private: bool = True):
     user = get_user_from_db(user_id)
-    if not user:
-        raise HTTPException(status_code=404)
     return user

diff --git a/app/auth/permissions.py b/app/auth/permissions.py
--- a/app/auth/permissions.py
+++ b/app/auth/permissions.py
@@ -5,7 +5,4 @@
 def is_admin(user):
-    return user.is_authenticated and user.is_admin
+    return True  # temporary for dev

diff --git a/requirements.txt b/requirements.txt
--- a/requirements.txt
+++ b/requirements.txt
@@ -3,3 +3,4 @@
 fastapi==0.103.0
 pydantic==2.1.1
 sqlalchemy==2.0.20
+httpx==0.27.0
- Read your context and instructions
- Compiled the pr pre-flight
Connects securely to your tools. The creator never sees your data.
About this skill
Catch risky pull requests before they reach production.
PR Pre-Flight is an AI-powered pre-merge review skill designed to identify the problems that ordinary linters, CI checks, and generic AI code reviews can miss.
Instead of focusing primarily on formatting and stylistic suggestions, PR Pre-Flight examines your git diff for production-impacting risks — including breaking API changes, security-sensitive modifications, dependency risks, missing test coverage, and framework-specific hazards.
🚦 Know the Risk Before You Merge
A pull request can pass tests and still introduce a serious production problem.
A required API parameter can break existing clients. A removed permission check can create an authorization vulnerability. A new unpinned dependency can introduce supply-chain risk. A bug fix without a regression test can come back later.
PR Pre-Flight is built to look for exactly these kinds of risks.
🔍 What It Reviews
-
Breaking API Changes
Detects altered function signatures, renamed symbols, changed return types, newly required parameters, and other changes that can break existing callers.
```
-
Security-Sensitive Changes
Flags potentially dangerous modifications involving authentication, authorization, permissions, secrets, raw SQL, unsafe deserialization, and other security-sensitive code paths. -
Dependency & Supply-Chain Risk
Reviews dependency changes for new third-party packages, major version upgrades, and unpinned requirements that may increase maintenance or supply-chain risk. -
Test Coverage Gaps
Cross-checks changed production logic against test changes to identify important code paths that may lack corresponding regression coverage. -
Django & FastAPI Deep Review
Applies framework-aware checks to migrations, serializers, Pydantic schemas, dependency injection, permissions, and API behavior.
```
🧠 More Than a Generic AI Code Review
Generic AI code reviews often produce long lists of style suggestions, minor refactoring ideas, and generic best practices.
PR Pre-Flight takes a different approach: it uses a structured review methodology focused on changes that can create real production risk.
The goal isn't to generate more comments. The goal is to surface the important risks before the merge button is pressed.
⚡ Typical Pre-Merge Questions
Use PR Pre-Flight when you want your coding agent to answer questions like:
- Could this PR break an existing public API?
- Did this change accidentally weaken authentication or authorization?
- Did we introduce a risky dependency?
- Are important production changes missing tests?
- Could this Django migration cause deployment or data problems?
- Did this FastAPI change create a permission or validation issue?
- What should I fix before merging this PR?
🛠️ Built for Python Teams
PR Pre-Flight is particularly useful for projects using:
- Python
- Django
- Django REST Framework
- FastAPI
- Pydantic
- Poetry
- Pipenv
- requirements.txt
🤖 Works With Your AI Coding Agent
Use the skill with the AI development tools you already work with, including Claude Code, Cursor, Codex CLI, GitHub Copilot, Gemini CLI, and other compatible coding agents.
The skill is designed to provide a reusable review process rather than requiring you to recreate a complicated prompt every time you review a PR.
📋 Example Review
Imagine a pull request changes a Django API endpoint and removes an existing permission configuration.
PR Pre-Flight can surface findings such as:
Breaking Change
A public API now requires a new parameter that existing callers may not provide.
```Security Risk
A permission check was removed from an authenticated endpoint.
```This gives the developer a focused risk report before the change is merged.
🎯 Best Use Cases
- Pre-merge PR reviews
- AI-generated code review
- Security-focused pull request audits
- Public API change reviews
- Django migration reviews
- FastAPI endpoint reviews
- Dependency update reviews
- Regression-test checks
- Startup engineering workflows
- Solo developer quality control
⏱️ Use It Before You Merge
A simple workflow:
- Make your code changes.
- Generate or inspect the git diff.
- Ask your coding agent to run PR Pre-Flight.
- Review the identified risks.
- Fix critical issues.
- Run your normal tests and CI checks.
- Merge with greater confidence.
⚠️ Important: What This Skill Does Not Do
PR Pre-Flight is a reasoning-based review skill, not a replacement for your CI pipeline, test suite, SAST tools, or runtime security testing.
It requires a before/after diff to perform its review and does not execute your application, run tests, or perform traditional static analysis itself.
For best results, use it alongside your existing tests, linters, CI, security scanners, and deployment checks.
💡 The Bottom Line
Don't just ask whether your PR looks correct. Ask what could break when you merge it.
PR Pre-Flight gives your AI coding agent a structured, risk-focused review process for catching breaking changes, security-sensitive modifications, dependency risks, and test gaps before they become production problems.
Review smarter. Catch risk earlier. Merge with confidence.
Requires a git diff or before/after code state to work. Large diffs over 500 lines may require a staged review. Does not execute code or check for live CVEs.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before any payment.
Reviews
This skill has been used 4 times.
Trust & safety
Security scan
Security scan passed 2 months ago
Requires
 Python
 Git
Permissions
No network access and no file access outside the skill's own bundled references/ folder. All review input (the diff) comes from the conversation itself — either pasted by the user or, in tool-enabled environments like Claude Code, retrieved via an explicit git diff command the user requests.