More screenshots
Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 Muse
 Dots+21 moreClaude CodeCursorCodex CLIMuseDots
 Manus
 Grok
 Grok Bot+18 agents
jwt token risk analyzer
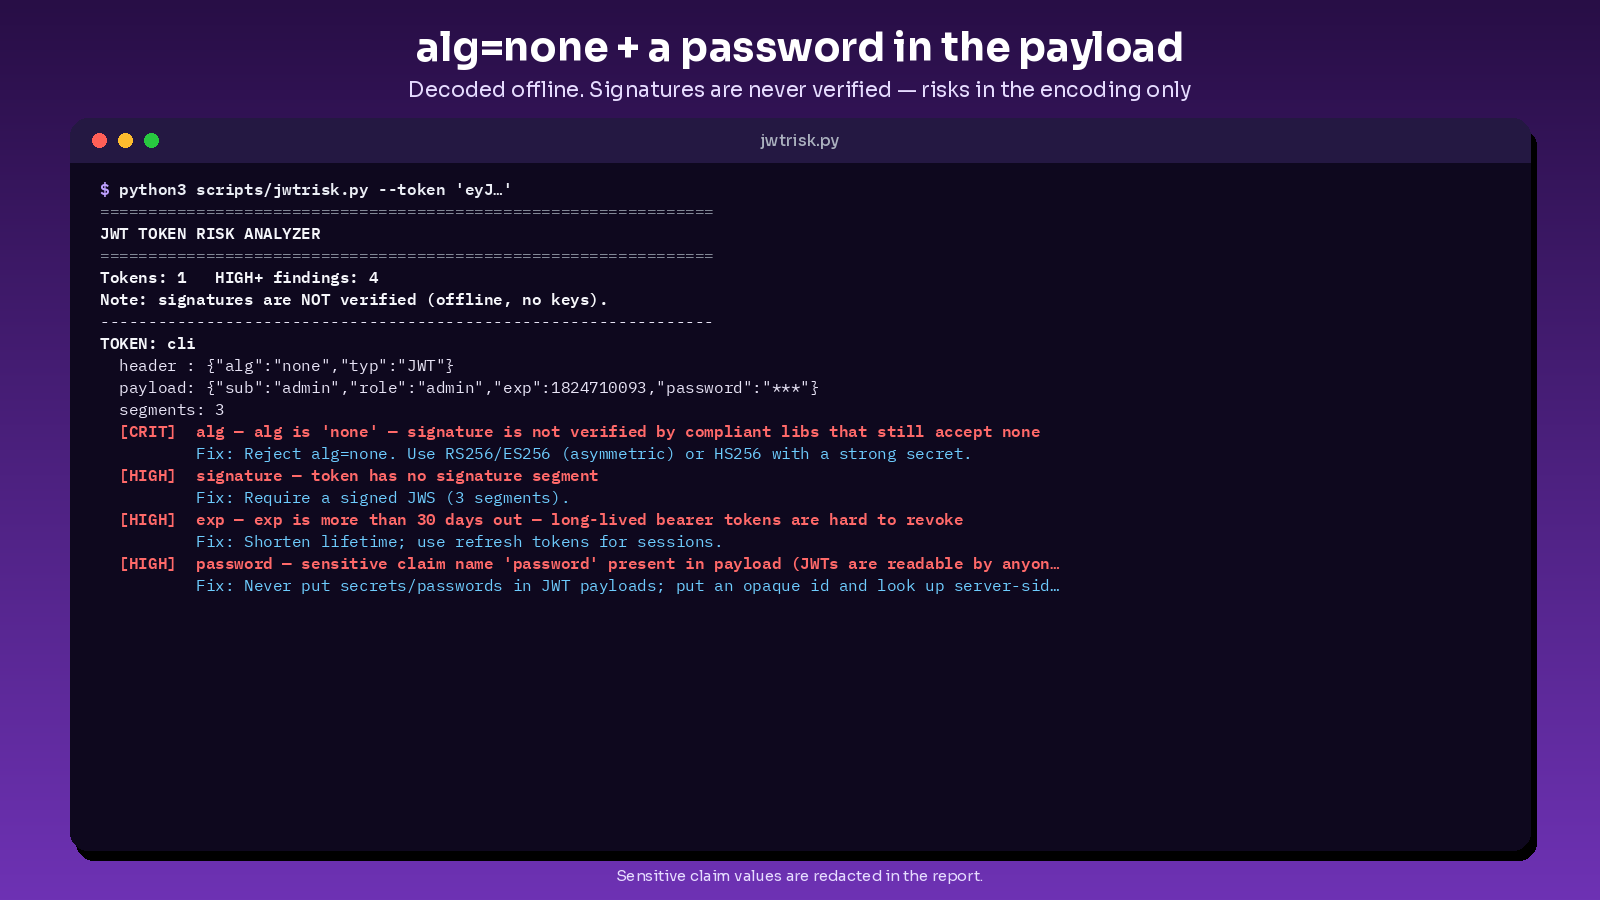
Decode JWTs offline and flag alg=none, missing exp, long lifetimes, kid path tricks and secrets in the payload. Does not verify signatures.
$5

jwt token risk analyzer
Example session with this skill installed
Analyze this token for risks: eyJhbGciOiJub25lIiwidHlwIjoiSldUIiwia2lkIjoiLi4vLi4vLi4vZXRjL3Bhc3N3ZCJ9.eyJzdWIiOiIxMjM0NTY3ODkwIiwibmFtZSI6IkpvaG4gRG9lIiwiaWF0IjoxNTE2MjM5MDIyfQ.
- Read your context and instructions
- Compiled the jwt token risk
- Generated the document
I have analyzed the provided JWT for configuration and security risks. High-severity issues were detected in the header.
JWT Risk Analysis Report
| Component | Finding | Severity | Description |
|---|---|---|---|
| Header | alg: none | CRITICAL | Token allows no signature verification. An attacker can modify claims. |
| Header | kid traversal | HIGH | The kid field contains path traversal characters (../../). |
| Payload | Missing exp | HIGH | Token has no expiration claim. It may be valid indefinitely. |
| Payload | Sensitive Info | LOW | Standard PII (name) detected in payload. |
Technical Details
- Algorithm:
none - Key ID (kid):
../../../etc/passwd - Expiration: Not set
- Issued At: 2018-01-20 03:43:42 UTC
Next steps
- Switch to a secure signing algorithm like RS256 or HS256.
- Implement strict input validation on the
kidheader to prevent path traversal. - Add an
exp(Expiration Time) claim to limit the token's lifetime.
1793175091878-2l7m.png
PDF · document
Example file from a real run - the skill writes it into your workspace.
Connects securely to your tools. The creator never sees your data.
About this skill
Decode a bearer token offline and see every encoding risk before you ship it.
JWTs are readable by anyone who has them. This skill decodes header + payload (no keys, no network) and flags the risks that keep showing up in real breaches: alg=none, missing exp, 30+ day lifetimes, kid path traversal, jku/x5u header injection and secrets sitting in the payload.
What it does
- Accepts a single token or a file with one JWT per line (Bearer prefixes fine)
- Ranks CRITICAL / HIGH / MEDIUM findings with concrete fixes
- Redacts sensitive claim values in the report
- Markdown + CSV output; exit 0 when there are no HIGH findings
Who it's for
API and auth developers, security engineers reviewing tokens from logs or bug reports.
Limits
Does not verify signatures. Offline decode and heuristic risk only. Not legal advice.
What's included
SKILL.md: workflow, commands, how to explain findingsscripts/: the checker (stdlib Python) plus sharedseccommon.pyreferences/sources.md: specs and guidance citedexamples/: good and bad samples used in the demotests/: unit tests (Python 3.8 / 3.9 / 3.13)
Standard-library Python only. No API keys, no network calls, no installs.
- Offline / local files only — does not fetch live URLs or call cloud APIs.
- Heuristic checks; not a full substitute for a professional audit or pentest.
- Not legal advice and not a certification of compliance.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before any payment.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 20 days ago
Permissions
File Scopes
Fully offline. No subprocess, no network modules used for outbound calls, no credential access.