Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 Muse
 Dots+21 moreClaude CodeCursorCodex CLIMuseDots
 Manus
 Grok
 Grok Bot+18 agents
Dependency Upgrade Strategist
Plan a risky dependency or runtime upgrade: blast radius, ordering, verification and rollback.
$15

Dependency Upgrade Strategist
Example session with this skill installed
We are three majors behind on our web framework and Node is two versions old. Last attempt rotted on a branch for six weeks. Here is package.json and the import count.
- Read your context and instructions
- Compiled the dependency upgrade strategist
Worked example — illustrative data.
Upgrade plan: framework 14 to 17, Node 18 to 22
Verdict
412 import sites, 3 majors, 2 peer changes, plus a runtime move. Route: step through majors, runtime first. Effort 12 days. Main risk: the bundler change in major 16, which is not a version bump in practice.
Breaking changes
| Change | Affects us | Where | Effort |
|---|---|---|---|
| Removed data-fetching API | yes | 61 files | M |
| Default caching changed | yes | config | S, silent |
| New peer requirement | yes | lockfile | S |
| Node 20 floor | yes | CI, 2 images | M |
Sequence
| Step | Change | Verify | Rollback |
|---|---|---|---|
| 1 | Node 22, CI and images | full suite | revert image tag |
| 2 | Framework 15 | suite plus 3 journeys | revert commit |
| 3 | Framework 16 with bundler | canary error rate | flag off |
| 4 | Framework 17 | suite plus canary | revert commit |
Test coverage
72% of touched paths covered; checkout and auth are the thin spots, so both get a manual pass and a canary window.
Canary
5% of traffic for 24 hours, error rate and p95 against baseline, owned by platform on-call.
Post-upgrade
Remove the compatibility shim from step 2, update CI images, delete dead codemod output, and add a monthly upgrade slot so the next gap is smaller.
Connects securely to your tools. The creator never sees your data.
About this skill
Dependency upgrade plan: blast radius from real imports, upgrade order that compiles, test strategy and a rehearsed rollback.
Use this skill when:
- plan a major dependency upgrade
- a framework version is end of life
- work out what breaks if we upgrade
- sequence a multi-service migration
Who it's for: Maintainers of ageing services and platform teams.
Example request
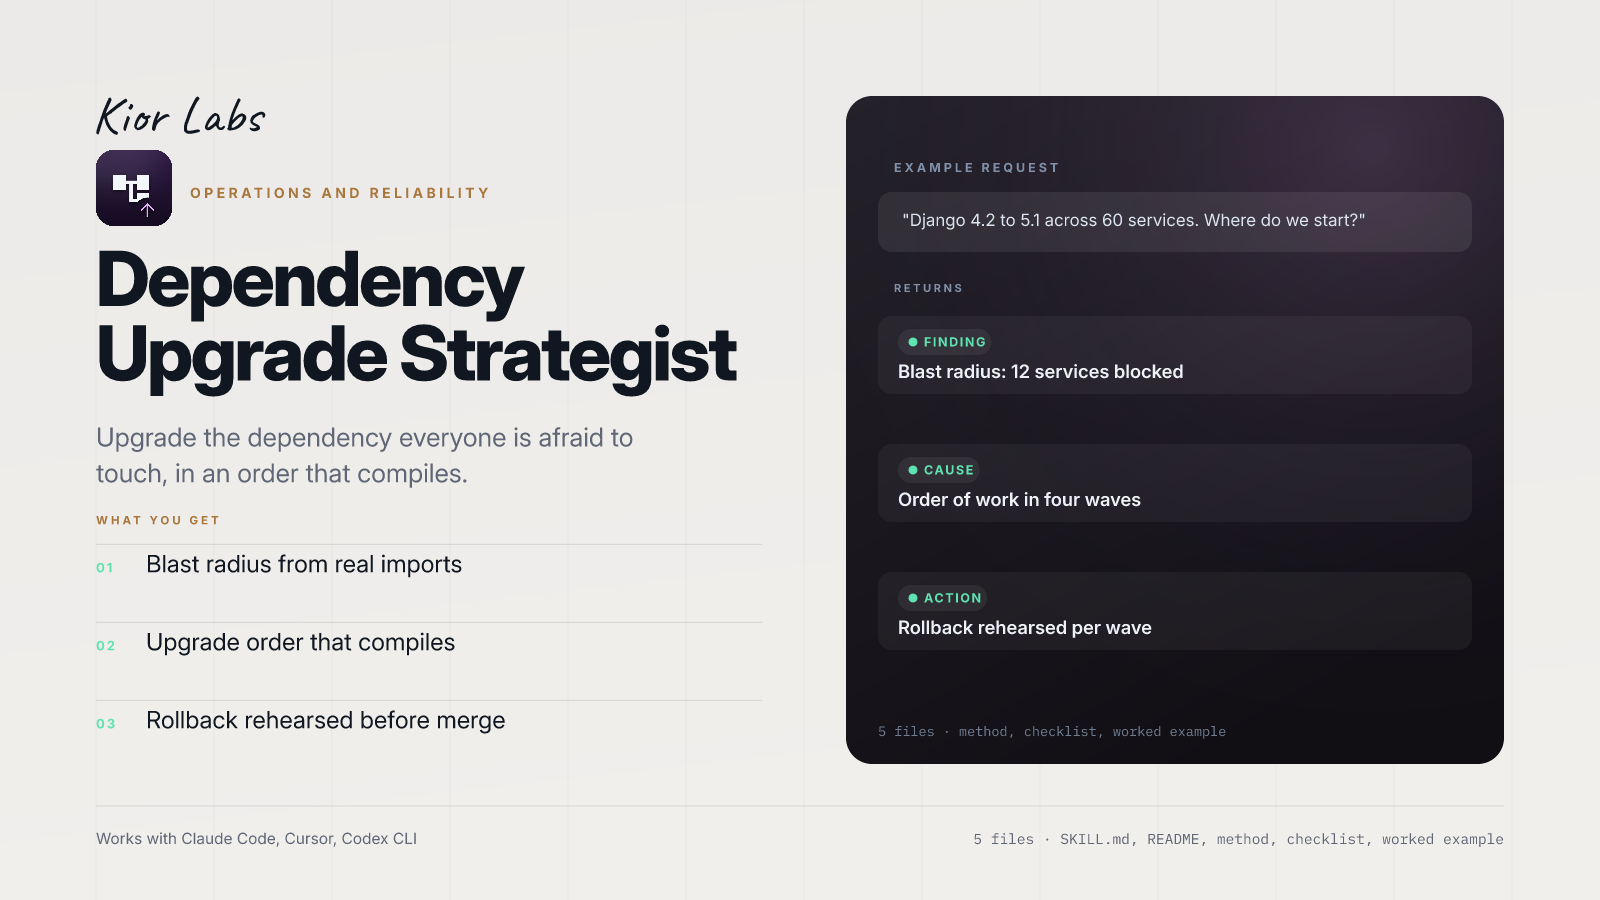
Django 4.2 to 5.1 across 60 services. Where do we start?
What the example returns
- Blast radius: 12 services blocked
- Order of work in four waves
- Rollback rehearsed per wave
In the package: five files — SKILL.md with the trigger and workflow, README.md, references/METHOD.md (the full method), references/CHECKLIST.md (the pass/fail gate) and examples/EXAMPLE.md (a worked run you can copy).
Works with Claude Code, Cursor, Codex CLI and any agent that reads SKILL.md. Plain markdown: no API key, no account, no network access.
Cannot execute code or run package managers. Risk assessment is limited to the code context provided. Does not automate the application of codemods.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before any payment.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 2 days ago