Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 Muse
 Dots+21 moreClaude CodeCursorCodex CLIMuseDots
 Manus
 Grok
 Grok Bot+18 agents
AI Supply Chain Attestation
Attest what runs in your AI stack: SBOM, provenance, signing and verification at install.
$19

AI Supply Chain Attestation
Example session with this skill installed
We use a hosted model, two MCP servers and about 300 npm packages. Compliance asked what is in our AI stack. Build the inventory and the attestation we can actually maintain.
- Read your context and instructions
- Compiled the ai supply chain
Worked example — illustrative data.
Supply chain attestation: support platform
Verdict
142 packages, 2 models, 3 MCP servers, 1 retrieval corpus. 9 items have no attestation: one MCP server is unpinned, two SDKs have no published SBOM.
Inventory
| Class | Count | Pinned | Owner |
|---|---|---|---|
| Code | 142 | 138 | platform |
| Models | 2 | 2 (dated snapshots) | ml |
| Data | 1 corpus | snapshot weekly | knowledge |
| Config | 6 prompts, 14 tools | git | product |
SBOM
CycloneDX per build from the lockfile, stored with the artefact, diffed between releases.
Provenance
CI builds from tagged commits; attestation records commit, builder, inputs, output digest. Published with every release.
Signing
Releases signed with a CI-held key; verification at deploy fails closed for anything with write access.
MCP servers
| Server | Version | Tools | Network |
|---|---|---|---|
| orders | pinned commit | 4 | egress to orders API only |
| docs | latest (fix) | 2 | none |
Policy
No unpinned dependency merges; new MCP server requires source review and re-review on tool description change.
Gaps
Two SDKs publish no SBOM; documented as accepted risk with a quarterly check.
Connects securely to your tools. The creator never sees your data.
About this skill
AI supply chain attestation: SBOM, provenance and signing plan for models, packages and MCP servers, with verification steps for buyers.
Use this skill when:
- produce an SBOM for AI packages
- prove where a model or MCP server came from
- sign artefacts before release
- answer a procurement security questionnaire
Who it's for: Platform and compliance teams shipping AI dependencies.
Example request
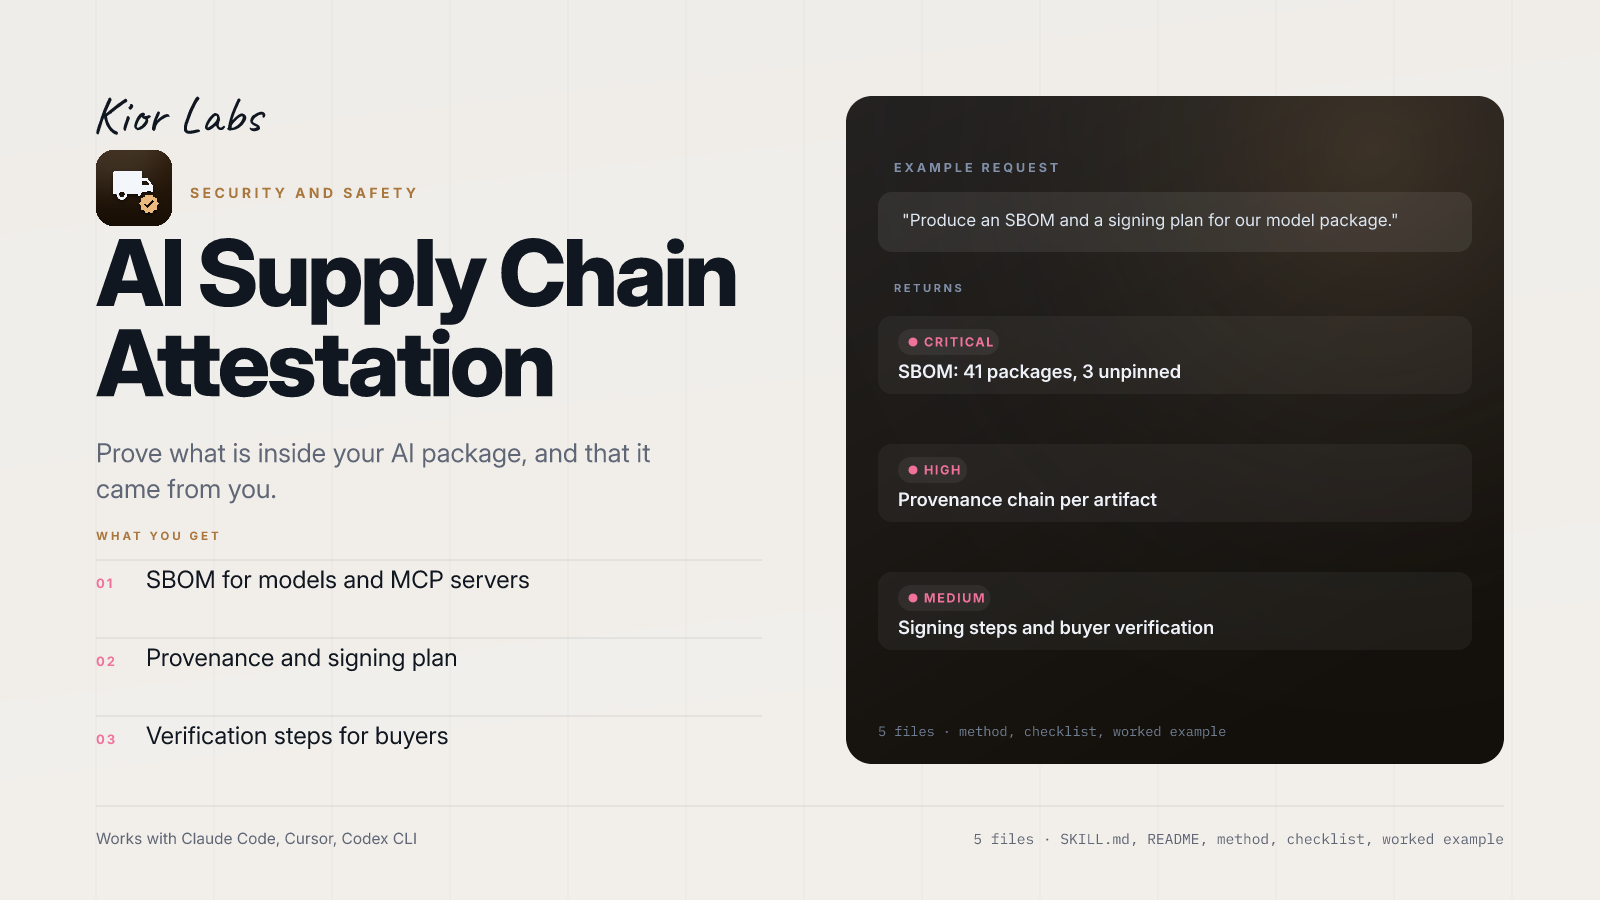
Produce an SBOM and a signing plan for our model package.
What the example returns
- SBOM: 41 packages, 3 unpinned
- Provenance chain per artifact
- Signing steps and buyer verification
In the package: five files — SKILL.md with the trigger and workflow, README.md, references/METHOD.md (the full method), references/CHECKLIST.md (the pass/fail gate) and examples/EXAMPLE.md (a worked run you can copy).
Works with Claude Code, Cursor, Codex CLI and any agent that reads SKILL.md. Plain markdown: no API key, no account, no network access.
Does not perform active vulnerability scanning. Requires CI/CD access for signing. Limited to creating the plan, not executing shell commands to generate files.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before any payment.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 2 days ago
Permissions
Works only from material you provide. No network calls, no credentials.